
Europe is in the middle of a digital reckoning. On one side, global competition, a widening innovation gap and fragmented regulation are all pressing in. On the other stands the foundation of the European model: rights, democracy, and a technological development that’s meant to serve people — not the other way around.
In Brussels, the Omnibus Package is talked about as a “clean-up.” But in practice, the package could become a historic test: can the EU simplify without dumbing down? Can it become easier to build AI systems — without making it easier to cause harm?
This article brings together five constructive proposals, drawn from interviews, expert commentary and concrete experience from municipalities, startup communities and regulatory researchers. The proposals rest on a basic principle that’s often overlooked in the regulation debate:
Europe has to be both innovative and democratic — and neither can be sacrificed for the other.
1. Clean up the overlap — but strengthen oversight
The EU’s digital regulation today is spread across silos: GDPR, the DSA, the DMA, the Data Act, NIS2 and the AI Act. The result is an unwieldy patchwork, where the same systems get hit with parallel requirements for audits, documentation and risk assessment.
The Commission’s focus on simplification isn’t without reason. An AI product today can face three or four different documentation requirements that cover almost the same ground. That’s neither efficient nor optimal for legal certainty.
The solution isn’t fewer requirements — it’s clearer ones.
Concrete steps:
- Merge documentation requirements across the GDPR and the AI Act, so companies fill out one combined risk-assessment module.
- Remove unnecessary duplicate requirements in the Data Act and the DSA that hit the same actors twice.
- Build stronger European and national oversight bodies that can actually understand and assess AI systems in practice.
As Paul Nemitz has put it: “without strong oversight, regulation loses its democratic legitimacy.”
Clean-up must therefore be followed by strengthened control, not weakened control.
2. Differentiate the requirements — without creating a “free pass” for big players
It’s true that small companies are hit harder by regulation than large ones. A Danish HR startup can spend months just working out how the GDPR interacts with the AI Act and the DSA — resources that could otherwise go toward development.
The Commission’s idea of proportionality therefore makes sense. But proportionality must not be confused with exemption.
High-risk AI is dangerous, regardless of company size.
Concrete steps:
For SMEs:
- Standardised templates for technical documentation.
- Lightweight audits for low- and medium-risk systems.
- Sandboxes where regulators actively advise startups.
For Big Tech:
- No relaxations.
- If anything, strengthened documentation obligations and risk reporting.
- Tighter oversight when advanced machine learning is used in public-sector or labour-market-related systems.
Andrea Renda often stresses that “smart regulation” isn’t about fewer rules, but about more targeted rules. That’s especially true here.
Proportionality should reduce burdens — not create loopholes.
3. A European digital master law — with rights at its core
Today, the EU’s digital regulation consists of many layers that overlap, collide with, or repeat one another. That creates a risk that both companies and authorities are navigating a landscape too fragmented to be effective.
The Omnibus Package is an opportunity to take the next step:
A unified European digital master law.
Not a new super-regulation, but a framework that provides structure and direction:
- clear rules on data responsibility and data processing
- a consistent ranking of AI risk categories
- common processes for documentation
- strengthened rights for citizens affected by automated decisions
This could form the foundation for a Digital Bill of Rights, something several European experts have called for. It would be a codification of Europe’s distinguishing trait: the right to privacy, the right to an explanation, the right to insight, and the right to be treated fairly by algorithms.
Europe shouldn’t give up its democratic model. It should strengthen it within a single, unified framework.
4. Eurostack: independence, not just innovation
Eurostack is often presented as a technical project — a European cloud for European data. But the project represents far more than infrastructure. It’s a geopolitical statement: Europe wants less dependence on AWS, Google and Microsoft.
Even the Draghi report points to the need for European capabilities that can support the continent’s own innovation and security. But independence comes at a price: governance.
The solution is clear:
Eurostack has to be democratic, transparent and accountable — not just European.
That means:
- clear requirements for data sovereignty
- audits that go beyond the minimum requirements in the AI Act
- full transparency on operations, security and risk
- no “regulatory exemption zones” for companies building on top of Eurostack
If Europe wants strategic technological sovereignty, Eurostack has to be more than a cloud — it has to be a digital common good.
5. Denmark: from rule-interpreter to rule-innovator
Denmark is often among the fastest to comply with EU rules, but not among the most active in shaping them. That’s a strategic weakness.
Denmark ought to be a frontrunner in responsible digital governance, AI transparency and ethical technology.
But the ASTA case showed that Denmark has challenges with control, documentation and the duty to explain when AI is used in practice.
Solution: Denmark should develop a “rights-first, compliance-light” model.
- help municipalities and regions comply with the AI Act and the GDPR through standardised guidelines
- build national competence centres for AI auditing
- create lightweight tools that SMEs can use to navigate regulation
- develop national test environments where startups can get pre-audits and regulatory sparring
That way, Denmark can move from being a good student to being a political force for innovation that helps shape Europe’s direction.
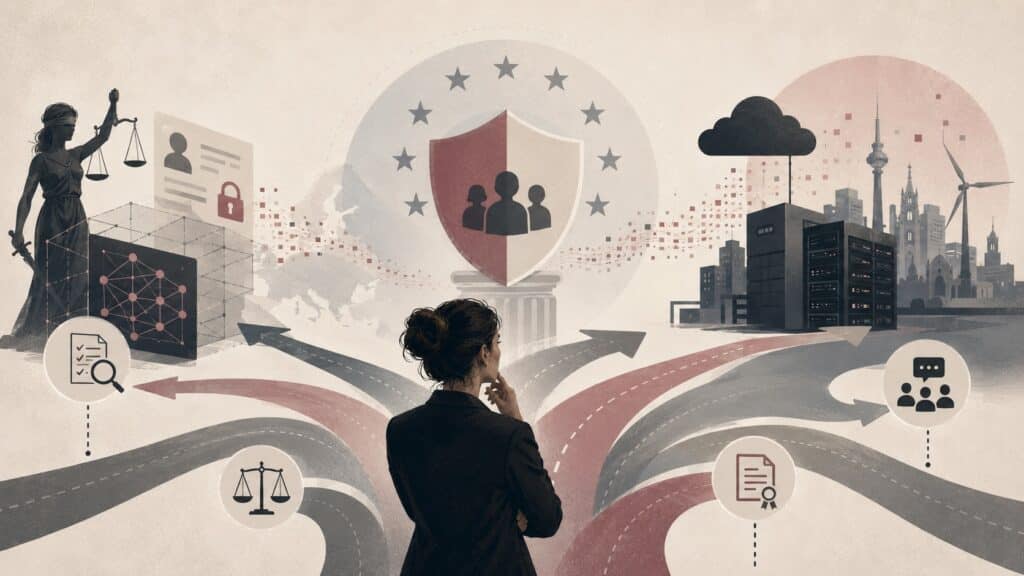
A Europe at a crossroads
The Omnibus Package isn’t just a technical clean-up. It’s an ideological reckoning over which digital story Europe wants to write going forward. Do we want to be the world’s strongest rights-based model — or a more open, risk-tolerant market that mimics the pace of the US?
The answer doesn’t have to be either/or. Europe can actually simplify and protect at the same time. It can strengthen innovation and strengthen oversight. It can create clearer frameworks for startups and greater security for citizens. It only requires one thing: regulation that’s smarter — not weaker.
Because in the end, Europe’s digital future isn’t about algorithms. It’s about values.
And none of those values should be sacrificed on the altar of innovation.
This article was previosly published on www.ai-portalen.dk